NIS-2 requires affected companies to actively manage cyber risks and implement appropriate protective measures. OIT provides support from analysis through to secure operation.
Challenge
New duties. Higher expectations. More responsibility.
New Legal Requirements
Cyber Risks and Threats
Technical and Organizational Measures
Reporting Requirements and Response Times
Verification and Documentation
Solution
From Analysis to Effective Implementation.
Impact Analysis & GAP Assessment
Technical Security Measures
Organizational Implementation
Monitoring & Incident Response
Documentation and Supporting Evidence
Advantages
Security. Clarity. Control.
Meeting Requirements in a Structured Way
Reduce Security Risks
Ensuring Business Continuity in an Emergency
Clear Responsibilities and Procedures
Continuously Improving Security
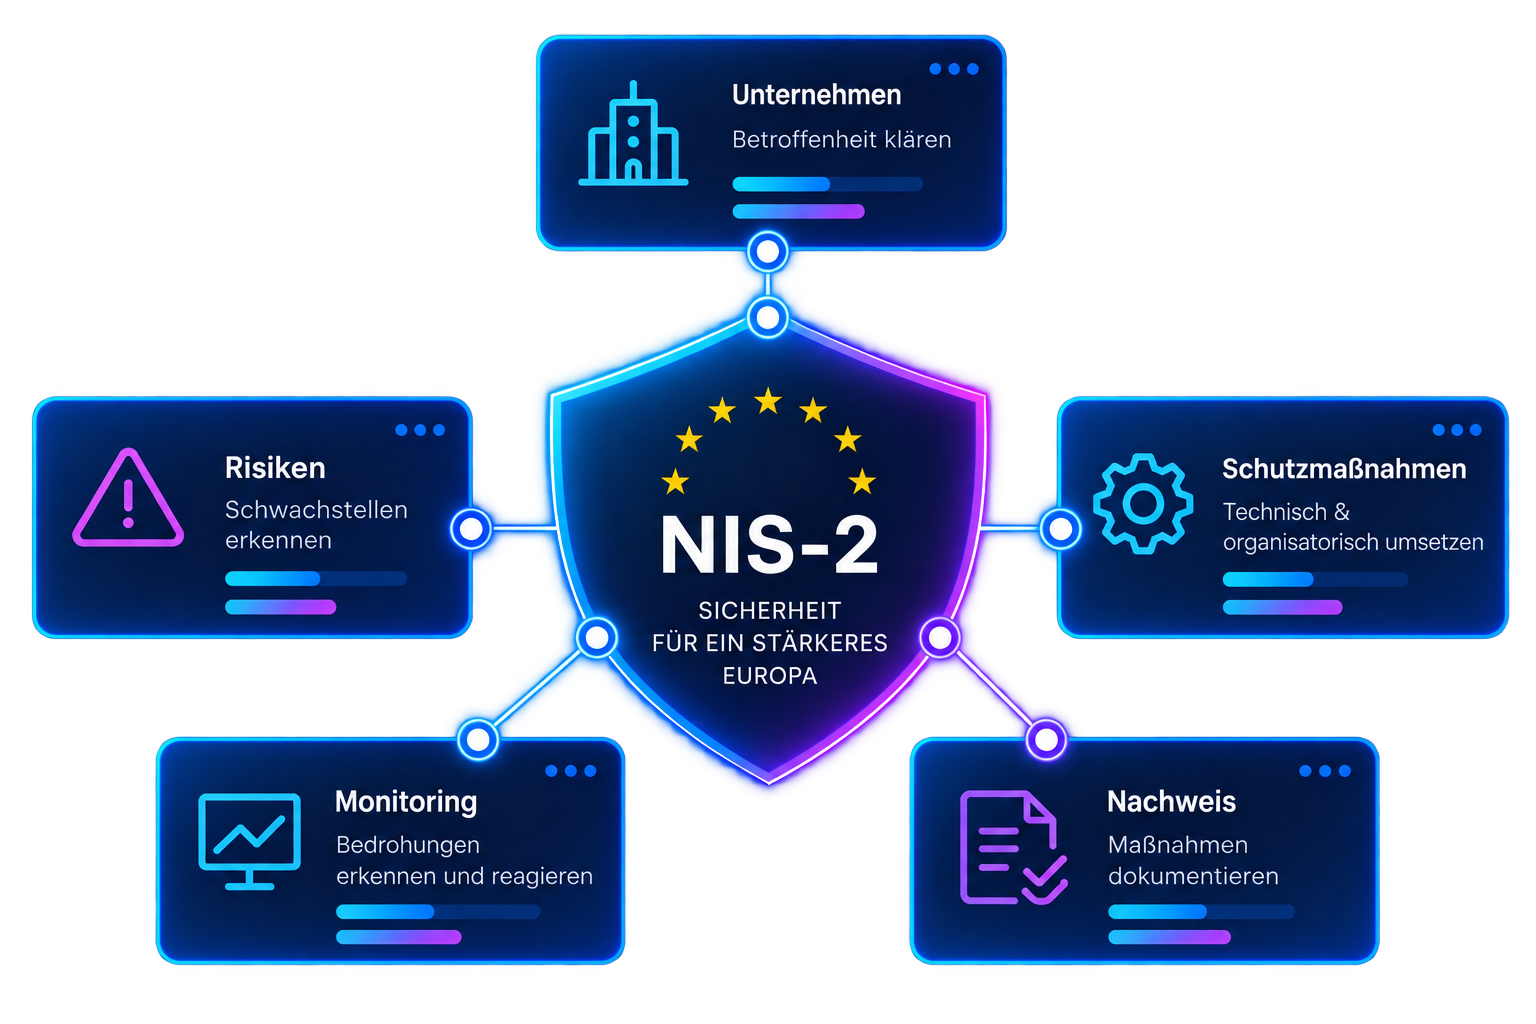
NIS-2 at a Glance
What NIS-2 Requires. And What Needs to Be Done Now.
NIS-2 imposes stricter requirements on companies in the areas of cybersecurity, risk management, and incident response. OIT provides support in these areas—with a pragmatic, technical, and experienced approach.
Understand
NIS-2 introduces new, mandatory requirements for security, risk management, and reporting obligations.
Check
We assess the extent of the impact and analyze your company's current security status.
Implement
We provide support in implementing technical and organizational measures—tailored to your needs and practical.
Operate
Security is an ongoing process. Monitoring, response, and continuous improvement are all part of day-to-day operations.
OIT Products. Integrated Security.
NIS-2 Security
OIT helps companies meet NIS 2 requirements and implement cybersecurity measures in a technically effective and sustainable manner.
OIT detects and analyzes attacks worldwide in real time. When a system detects a threat, that information helps protect the entire network.
36 server locations. A safety net.
LIVE FROM OIT INFRASTRUCTURE
Case studies
AI verifies 15,000 emails/hour for mid-sized companies
ZeroTrust Mail combines proven mail security with AI-powered analysis – for automated, traceable, and reliable defense against spam, phishing, and other email threats in the enterprise environment.


 German
 English
